
Audit Log
Field-level before/after history. The forensic record of who changed what, when.
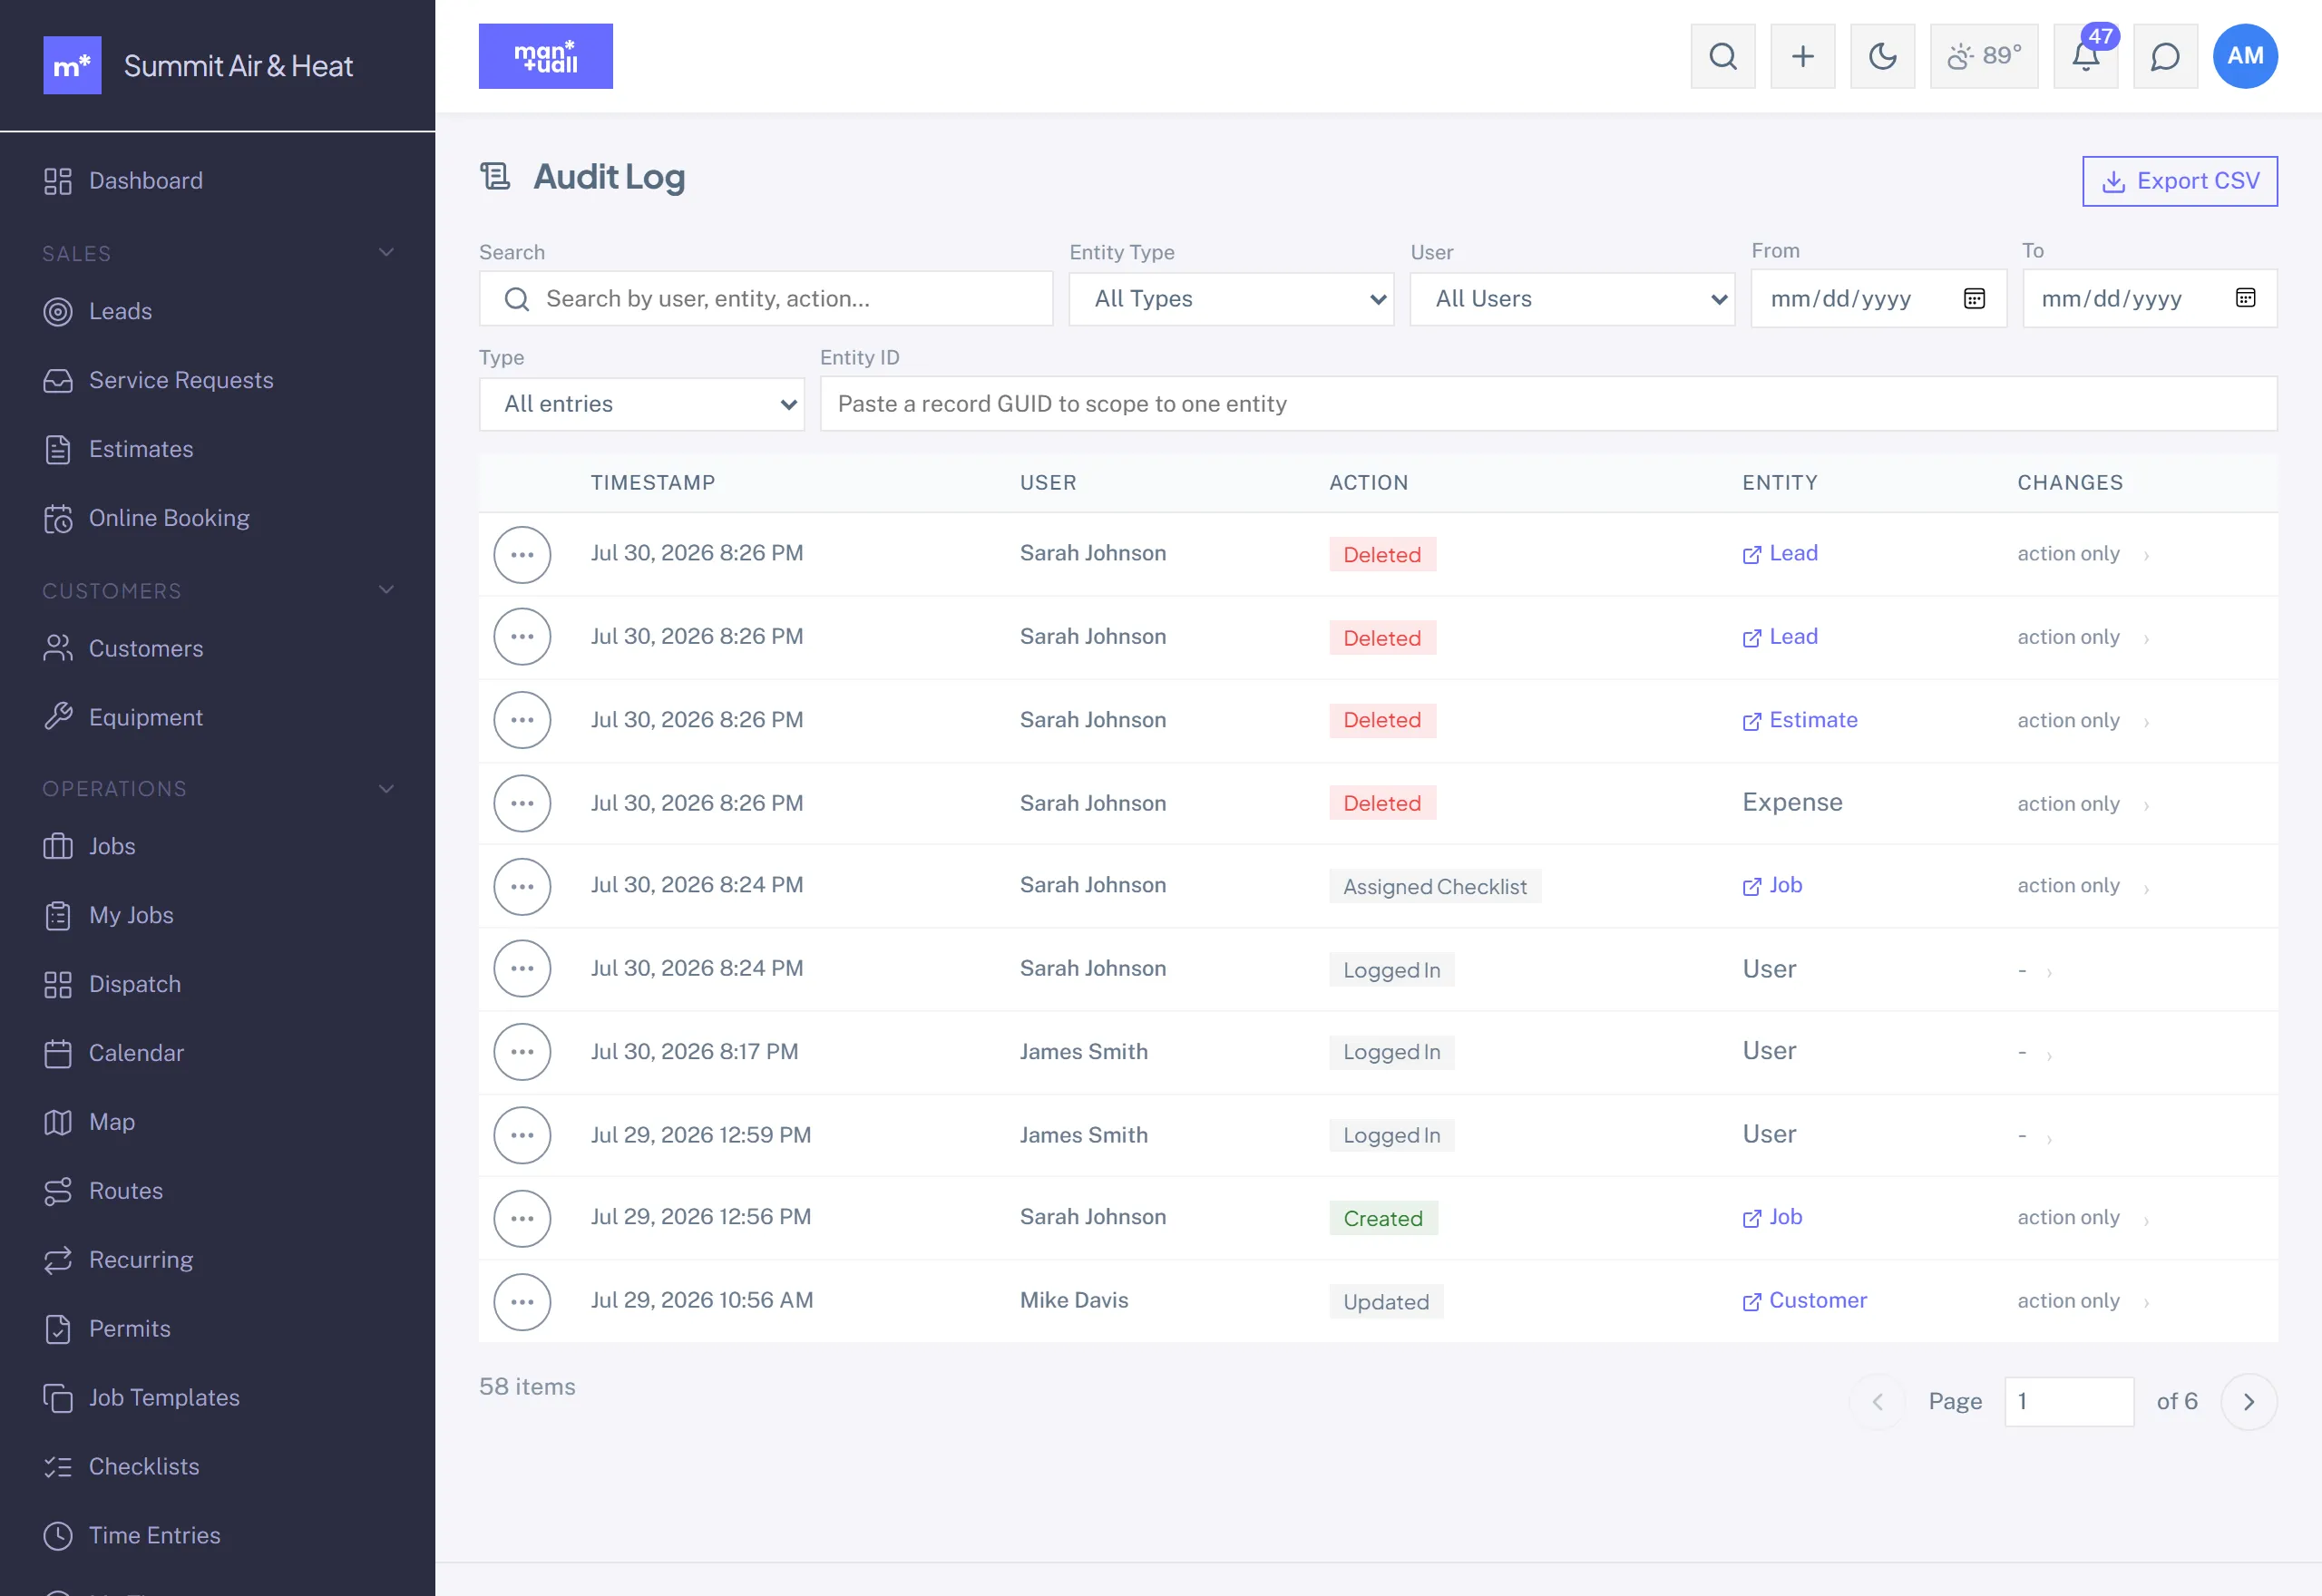
The Audit Log is the field-level before-and-after record of every change. It's distinct from the Activity Log, the higher-level event stream that powers the dashboard feed.
What gets logged
- Every update on an audited record: who changed which field, from what to what, and when.
- Deletes (soft and hard).
- Status changes.
- Permission changes on role definitions.
What doesn't
- Reads. The Audit Log is write events only.
- Internal computed changes (for example a recurring schedule advancing its next run date).
Where it lives
Sidebar -> Insights -> Audit Log. Filter by entity type, user, or date range. Each row expands to show the field-level diff, and the detail page carries the full change list plus a snapshot of the record after the change. You can also pull an entity's history straight from its own detail page.
Use cases
- Forensic: "Who deleted this customer?" "Who changed the tax rate yesterday?"
- Disputes: "When was the invoice amount last edited?"
- Coaching: "How often do techs edit time entries after the fact?"
Retention
Append-only and retained for the life of your workspace, so the forensic trail is always there when you need it.
Plan tier
Audit Log is on Business.